Breaking
Latest tech news from South Africa and around the world•Stay updated with breaking technology developments•Innovation and digital transformation news•AI, gaming, and gadget updates daily•Crypto and fintech news from Africa•
 SA Tech News Desk
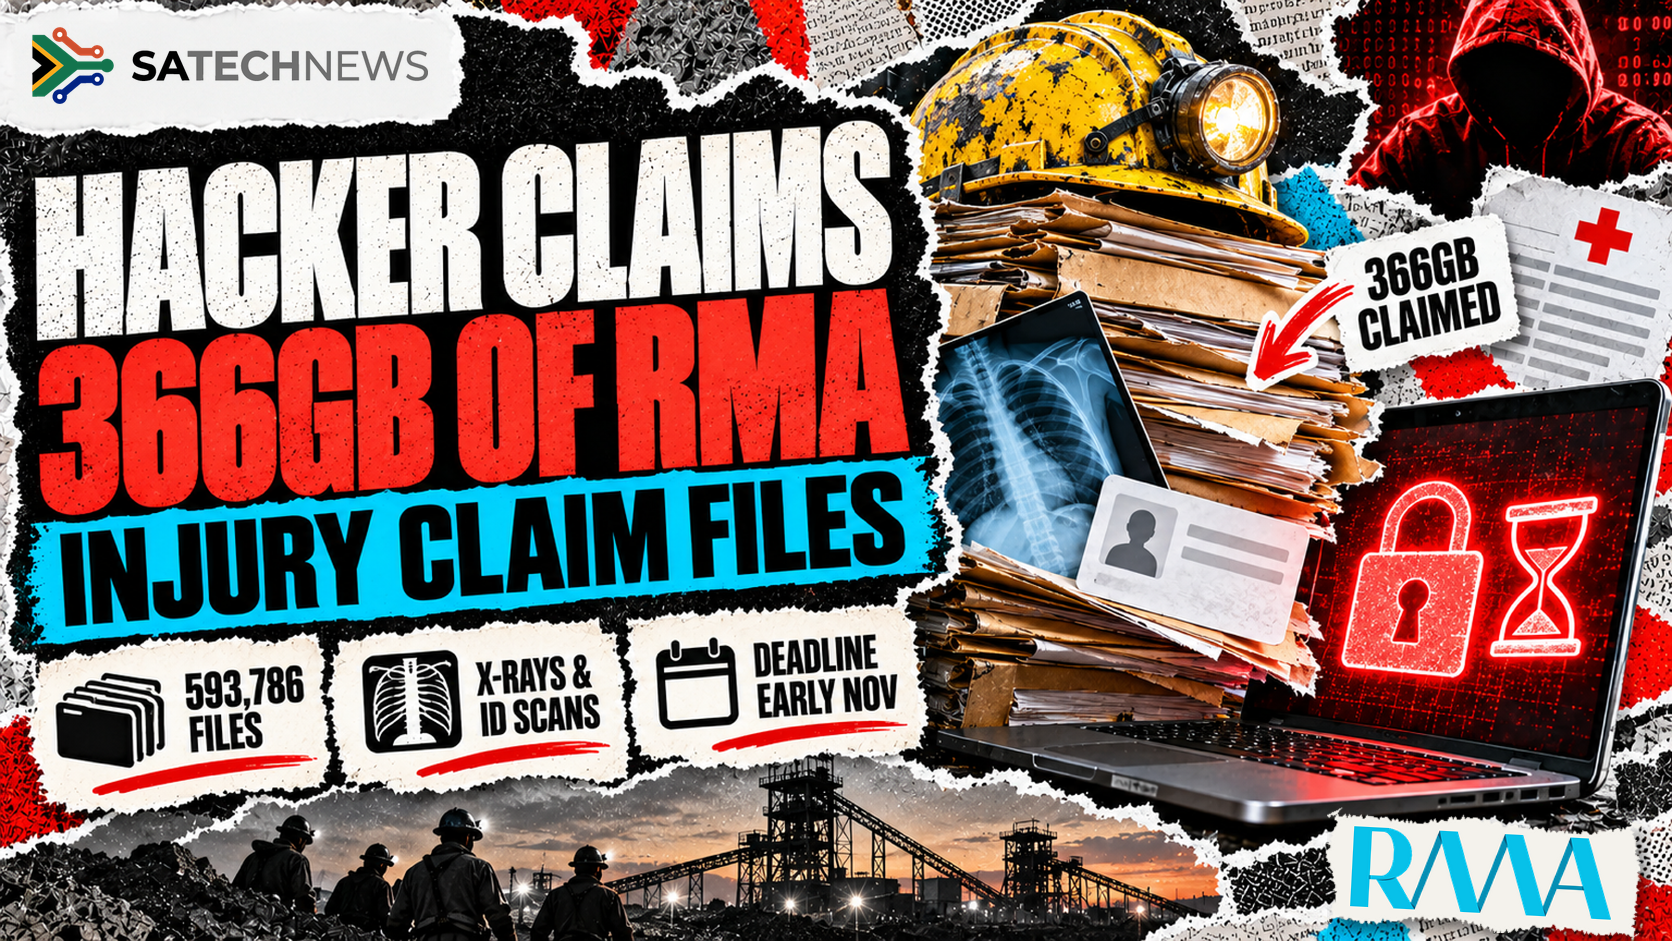
Rand Mutual Assurance is investigating a hacker's claim to hold 366GB of injury-claim data on miners and metalworkers, with a ransom due in early November.
Rand Mutual Assurance (RMA), which handles workplace injury and disease claims for South Africa's mining and metals industries, is investigating a claim that a hacker has stolen 366GB of its data. The listing, which surfaced on 23 October, says it holds about 1.6 million compensation claim records and 593,786 other company files, and threatens to publish them unless a ransom is paid in early November.
RMA has confirmed only that it is looking into it. "Rand Mutual Assurance confirms it has received an alert about a data breach. Investigations are underway," chief information security officer Nduduzo Majozi told MyBroadband. He said RMA would say more once the investigations were concluded. The statement does not confirm that data was taken and does not address the ransom demand.
The people in those files have a lot to lose. A compensation claim can carry an injured worker's ID number, medical reports and the bank details used to pay them. MyBroadband, which reviewed sample data from the listing, said it included scanned ID cards, insurance claim documents, X-rays, medical certificates and material from psychologists.
RMA was founded in 1894 and is licensed under the Compensation for Occupational Injuries and Diseases Act to handle claims that would otherwise go to the state's Compensation Fund. It covers mining employers and, since 2015, iron, steel and metals employers, which register with RMA rather than the Compensation Fund.
If the claim holds up, the exposed records belong mostly to miners and metalworkers who were hurt or fell ill at work. They did not pick RMA as a supplier: their employer's sector did.
The two local reports disagree on some details. TechCentral, citing the Dark Web Intelligence account on X that first flagged a post on an underground forum, reported 1.68 million records, a US$95,000 (about R1.6 million) demand and a 5 November deadline. MyBroadband, which found the listing on the leak site of a ransomware group called Kazu, reported about 1.6 million records, a US$98,000 (about R1.57 million) demand and a 4 November deadline. Both put the haul at 366GB and 593,786 files.
Dark Web Intelligence described the claims as unverified, and TechCentral said it had not seen the post or any sample data. It is not known when the alleged intrusion took place. A count of records is also not necessarily a count of people.
RMA is the latest South African insurer to face this kind of listing. In June a ransomware group breached MIP Holdings, a software supplier to insurers, and its chief executive said data belonging to customers of about 45 insurers had been taken. LegalWise, Samwumed and Edcon have since appeared on that group's leak site. MyBroadband named that group as The Gentlemen, and did not link it to the RMA listing.
Earlier this month a hacker claimed to hold 80 million records from pathology group Ampath, which said the figure referred to database entries rather than individual patients.
Under POPIA, an organisation must notify the Information Regulator and the people affected as soon as reasonably possible once there are reasonable grounds to believe their personal information was accessed by an unauthorised person. RMA has not said publicly whether it has notified the regulator.
RMA has not confirmed whether any data left its systems, how many claimants could be affected or how it will respond to the demand. It has not said whether claim payments or its online services have been disrupted. The listing gives RMA until 4 November, or 5 November by TechCentral's account, before the files are published.
Source: SA Tech News


